# Boilerplate: Clerk + Drizzle + Stripe Next shell, CVE-bumped to 16
Source: https://www.michaelchurley.com/blog/boilerplate-clerk-drizzle-stripe-next16-cve
Published: 2026-02-22
Author: Michael C. Hurley
Tags: boilerplate, nextjs, clerk, drizzle, vercel-postgres, stripe, catppuccin, hustlelaunch, saas-starter, cve, resend, michaelmonetized
## Who
I needed a reusable Next shell that already had Clerk protect, a subscriptions table, and a Stripe webhook. Empty create-next-app was the wrong starting line, and a Convex payment library was the wrong spine for this clone path.
For operators cloning a private Hustle Launch starter onto Vercel. Buyers of a polished marketing site can keep walking.
## What
I shipped **boilerplate**, private https://github.com/michaelmonetized/boilerplate. HEAD `6f2dd2f`. **63** commits. package **0.1.0**.
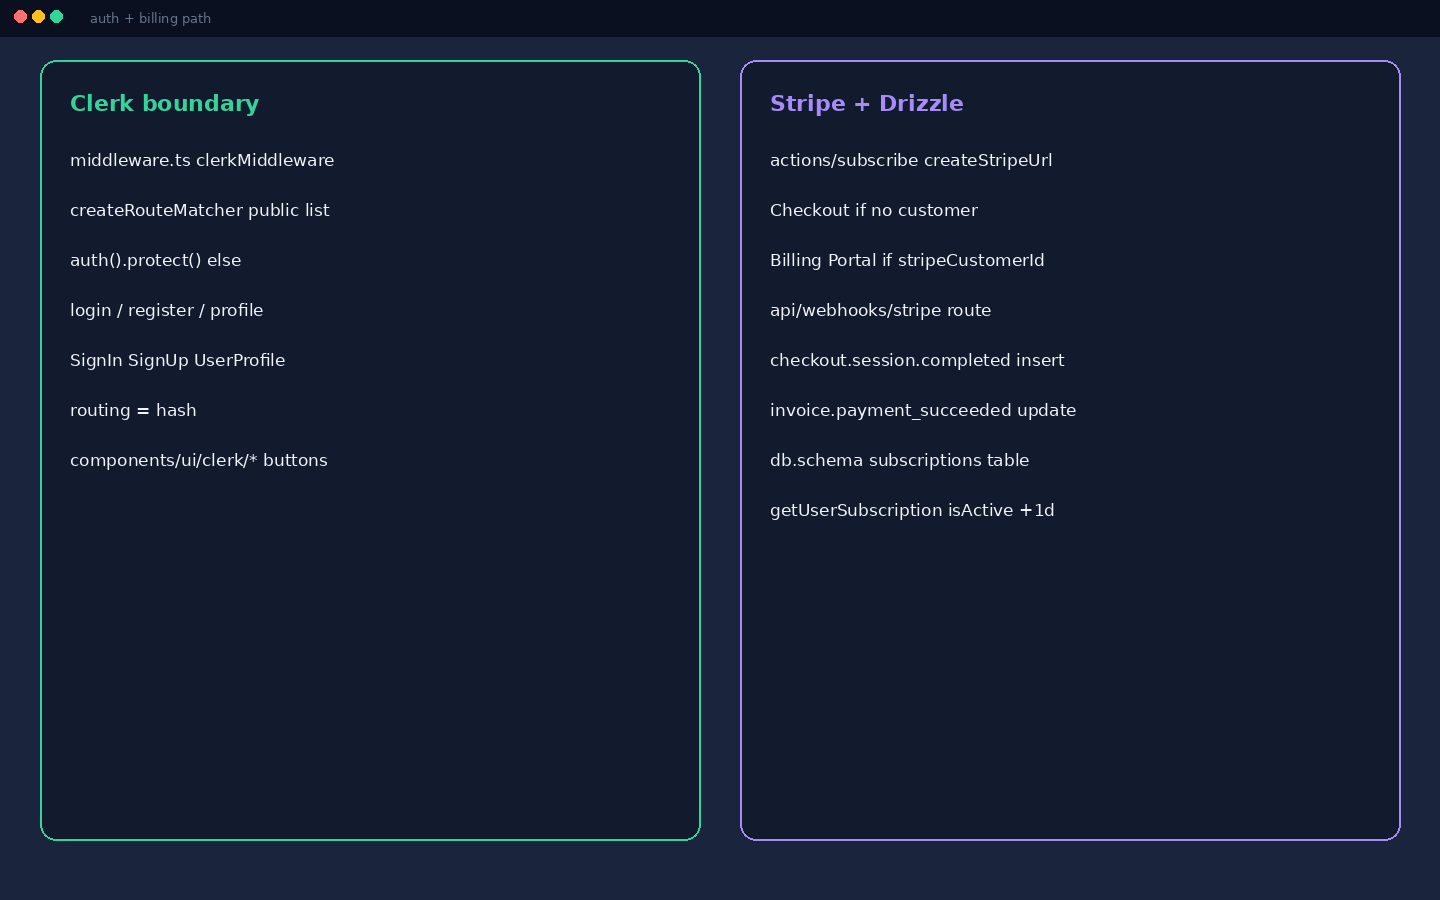
Stack that actually exists in tree: Next App Router, Clerk (SignIn/SignUp/UserProfile hash routing + clerkMiddleware public-route matcher), Drizzle on @vercel/postgres (subscriptions + error tables), createStripeUrl server action (Checkout or Billing Portal), Stripe webhook writing userId / customer / price / period end, Resend + react-email deps, Catppuccin latte/mocha CSS vars, custom max webfonts, filled privacy/terms/refunds.
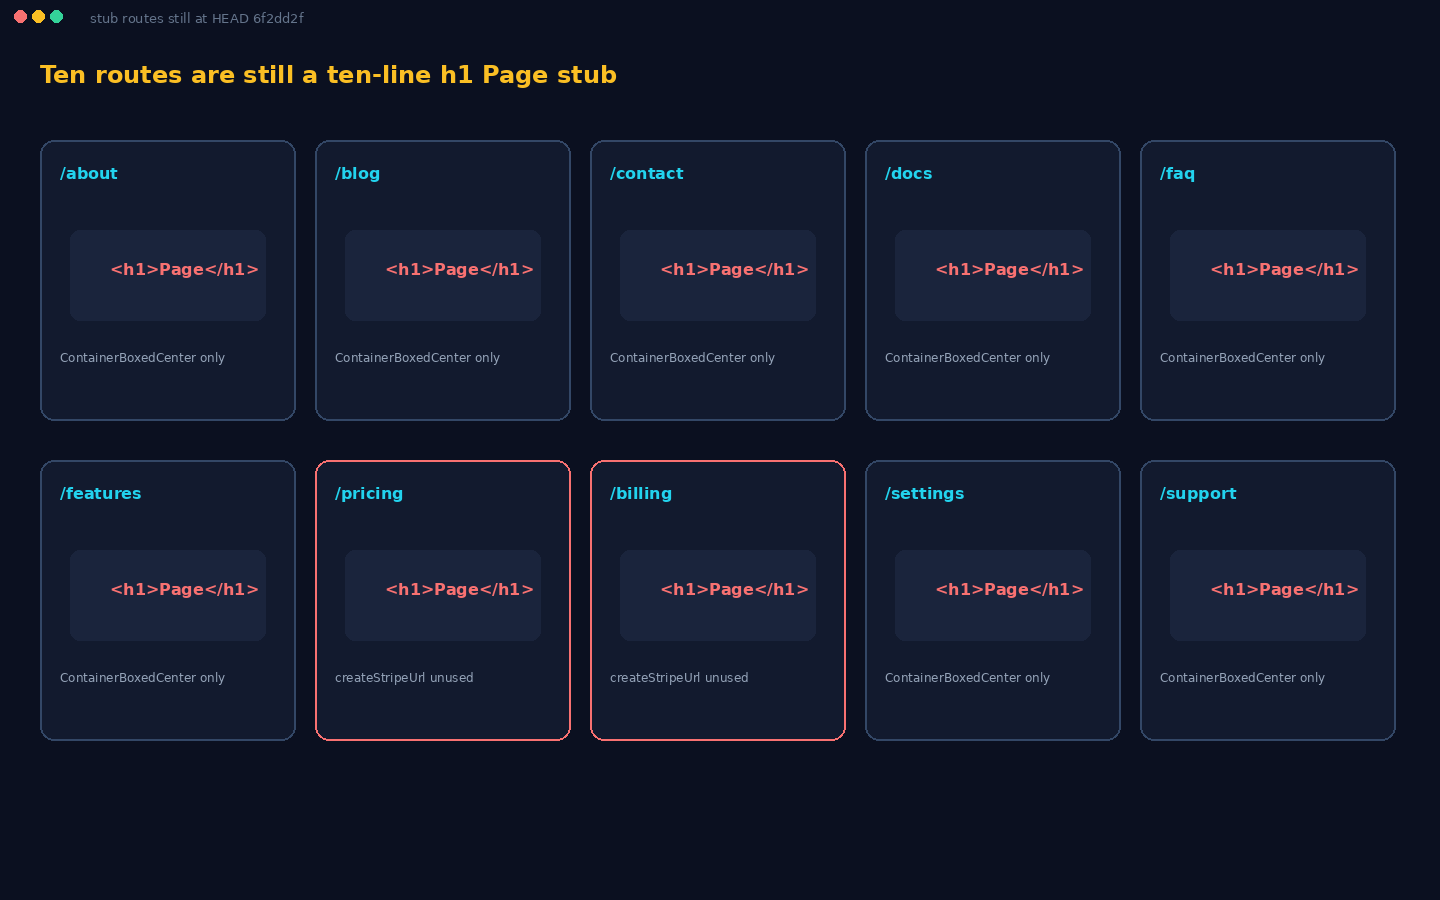
Honest day-one residue that is still at HEAD: about / blog / contact / docs / faq / features / pricing and protected billing / settings / support are each a ten-line Page
stub. /pricing does not call createStripeUrl. No tracked .env.example despite README. PLAN.md (Jan 2026) still lists Convex, PostHog, CLI scaffolding. .cursor/rules/STRIPE.md is Theo KV-sync essay pasted beside a Postgres webhook implementation.
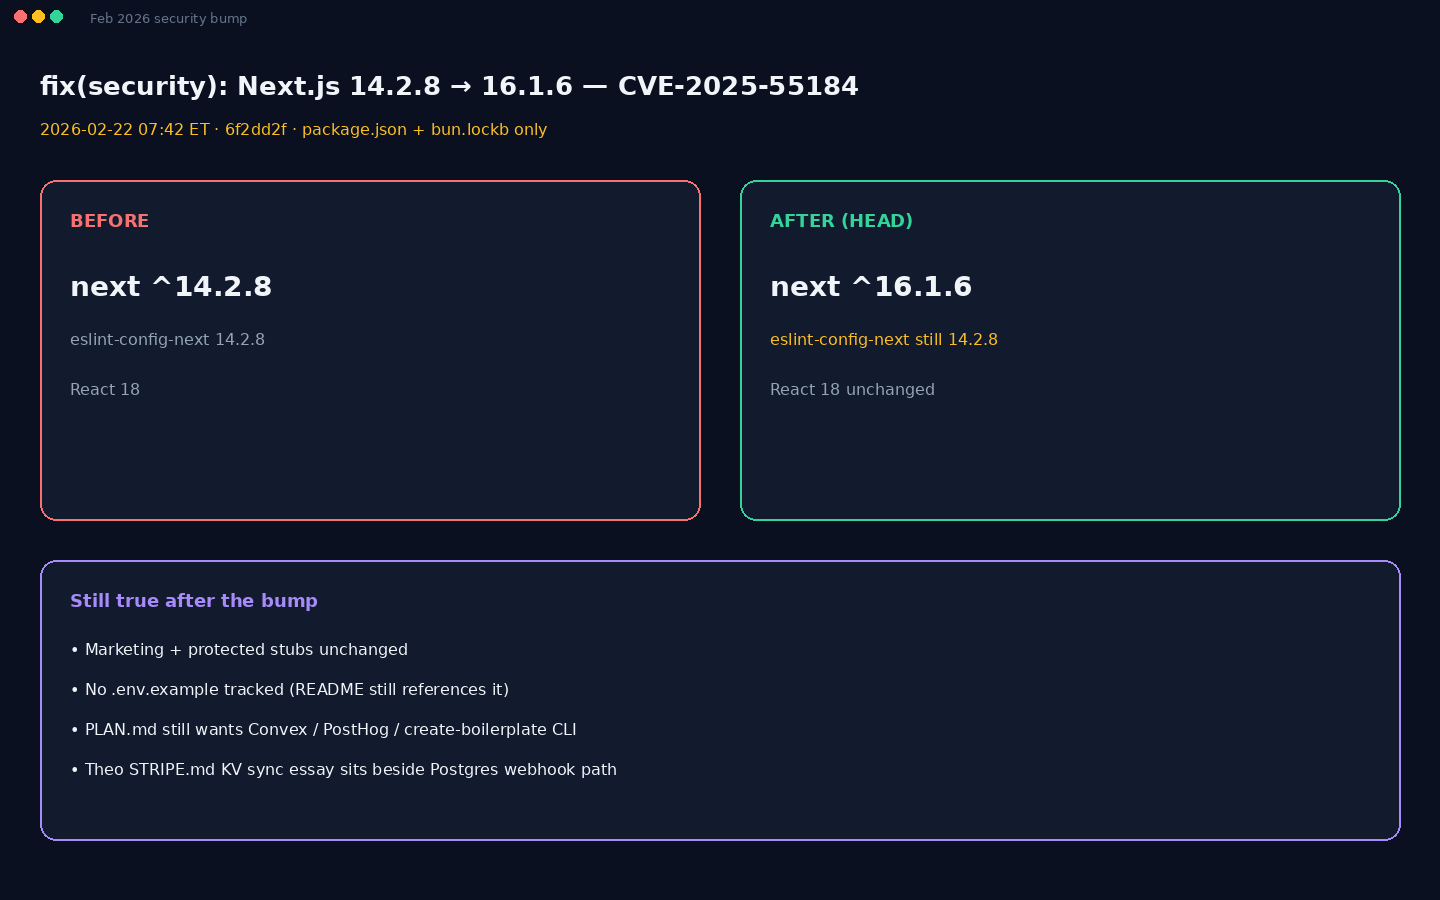
Feb 22 2026: fix(security) upgrade Next.js 14.2.8 to 16.1.6 for CVE-2025-55184. package.json + bun.lockb only. Live: https://boilerplate-fawn-gamma.vercel.app and https://boilerplate.hustlelaunch.com both 200 with Boilerplate.
## Where
Code: [github.com/michaelmonetized/boilerplate](https://github.com/michaelmonetized/boilerplate), private MIT.
Clone requires michaelmonetized auth. README still expects mv .env.example .env (file not tracked). Edit data/app.ts, install deps, deploy Vercel.
Live shells: [boilerplate-fawn-gamma.vercel.app](https://boilerplate-fawn-gamma.vercel.app) · [boilerplate.hustlelaunch.com](https://boilerplate.hustlelaunch.com)
## When
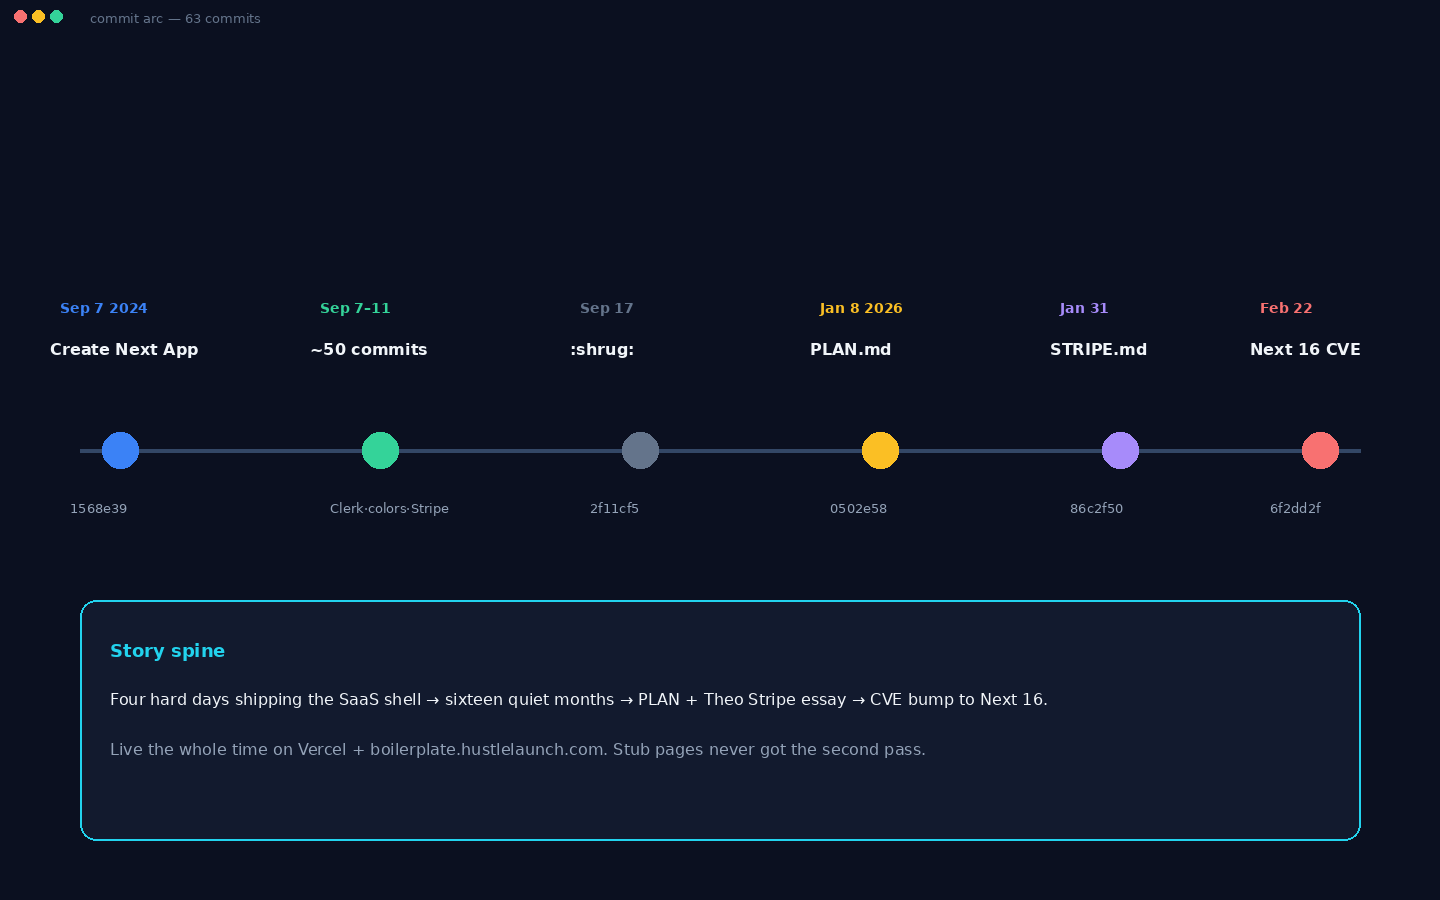
**2024-09-07 to 09-11 ET.** Create Next App, then Clerk middleware/redirect/color fights, then Stripe ready (~50 commits in four days).
**2024-09-17.** shrug.
**2026-01-08.** PLAN.md.
**2026-01-31.** STRIPE.md sync.
**2026-02-22 07:42 ET.** Next 16 CVE bump to HEAD `6f2dd2f`. Queue push **2026-02-22T12:42:54Z**.
## Why
A SaaS starter is only honest if the auth boundary, the subscriptions row, and the webhook exist, and if you admit the marketing routes are still stubs when you CVE-bump sixteen months later.
**Engagement Q:** Wire /pricing + /billing to createStripeUrl next, or replace the Postgres webhook with Theo single KV sync before cloning this into the next hustle?